Microsoft Defender for Endpoint
VerifiedEndpoint detection and response across Windows, Mac, Linux, iOS and Android
Is this your product? Rent a top-5 spot in Threat Hunting Software from $219 a month.
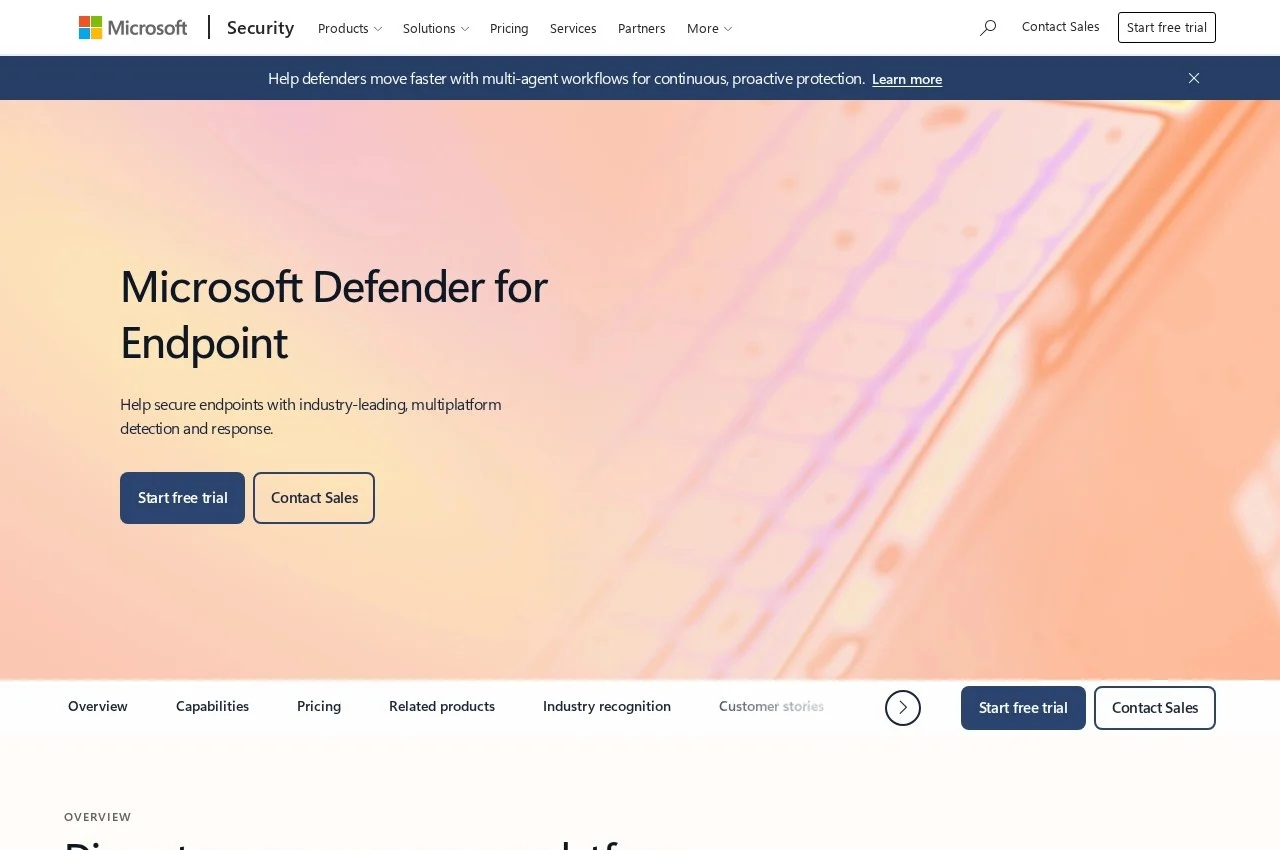 See all screenshots
- Deployment Cloud Based, SaaS
- Starting price Not published
- Free trial Available
- Best for Small Business, Medium Business, Large Enterprise
What is Microsoft Defender for Endpoint?
Microsoft Defender for Endpoint is endpoint security covering prevention, detection, investigation and response across Windows, macOS, Linux, iOS and Android, sitting within Microsoft's security range alongside Defender XDR, Entra for identity, Intune for device management, Purview for data governance, Sentinel for SIEM and Security Copilot.
Being built into Windows rather than installed onto it is the structural advantage and it is not a small one. The sensor ships with the operating system, so there is no agent to deploy on a Windows fleet, no compatibility matrix and no separate update mechanism, which removes the largest practical cost of endpoint security at scale.
Extending to Linux, macOS, iOS and Android matters because the advantage above evaporates on a mixed estate, and an organisation running significant non-Windows infrastructure is buying a competent cross-platform product rather than a native one, which is the comparison worth making honestly.
Licensing decides this purchase more than capability does, since Defender for Endpoint arrives inside Microsoft 365 E5 and is sold as standalone Plan 1 and Plan 2 tiers, so the real question for most organisations is what they already pay for rather than which product tests best. Microsoft publishes a security pricing overview covering the range.
Key Features of Microsoft Defender for Endpoint
- Endpoint detection and response
- Next generation antivirus prevention
- Automated investigation and remediation
- Threat and vulnerability management
- Attack surface reduction rules
- Built into Windows without an agent
- macOS, Linux, iOS and Android coverage
- Integration with Defender XDR
- Integration with Intune and Entra
- Threat analytics and hunting
- Security Copilot assistance
- Plan 1 and Plan 2 standalone tiers
Microsoft Defender for Endpoint Pricing
Within Microsoft 365 E5
Not published
Defender for Endpoint is included in Microsoft 365 E5, so most organisations acquire it through that licence rather than separately.
Plan 1 and Plan 2
Not published
Sold as standalone tiers with rates on Microsoft’s security pricing overview. No figure for either plan appears on the captured product pages.
Microsoft Defender for Endpoint Specifications
- Deployment
- Cloud Based
- SaaS
- Desktop
- Windows
- Mac
- Linux
- Web App
- Mobile
- iOS
- Android
- Built for
- Small Business
- Medium Business
- Large Enterprise
- Support
- Phone
- Knowledge Base
- Public API
- Yes
- Free trial
- Yes
- Free plan
- No
- Runs in browser
- No
- Customisable
- No
- Website
- microsoft.com
Microsoft Defender for Endpoint Screenshots
Microsoft Defender for Endpoint Comparisons

Your experience counts
Rate Microsoft Defender for Endpoint
Used Microsoft Defender for Endpoint? Your honest review helps the next buyer decide. It takes about three minutes.
Thanks, your review is in.
Our editors check every review before it goes live, usually within 2 business days.
Microsoft Defender for Endpoint FAQs
Alternatives to Microsoft Defender for Endpoint
Other Endpoint Detection And Response (EDR) Software recorded on the same fields.