Semgrep
VerifiedCode scanning with rules written in the syntax of the code itself
 See all screenshots
- Deployment Cloud Based, On Premise
- Starting price Free
- Free trial Available
- Best for Freelancers, Small Business, Medium Business
What is Semgrep?
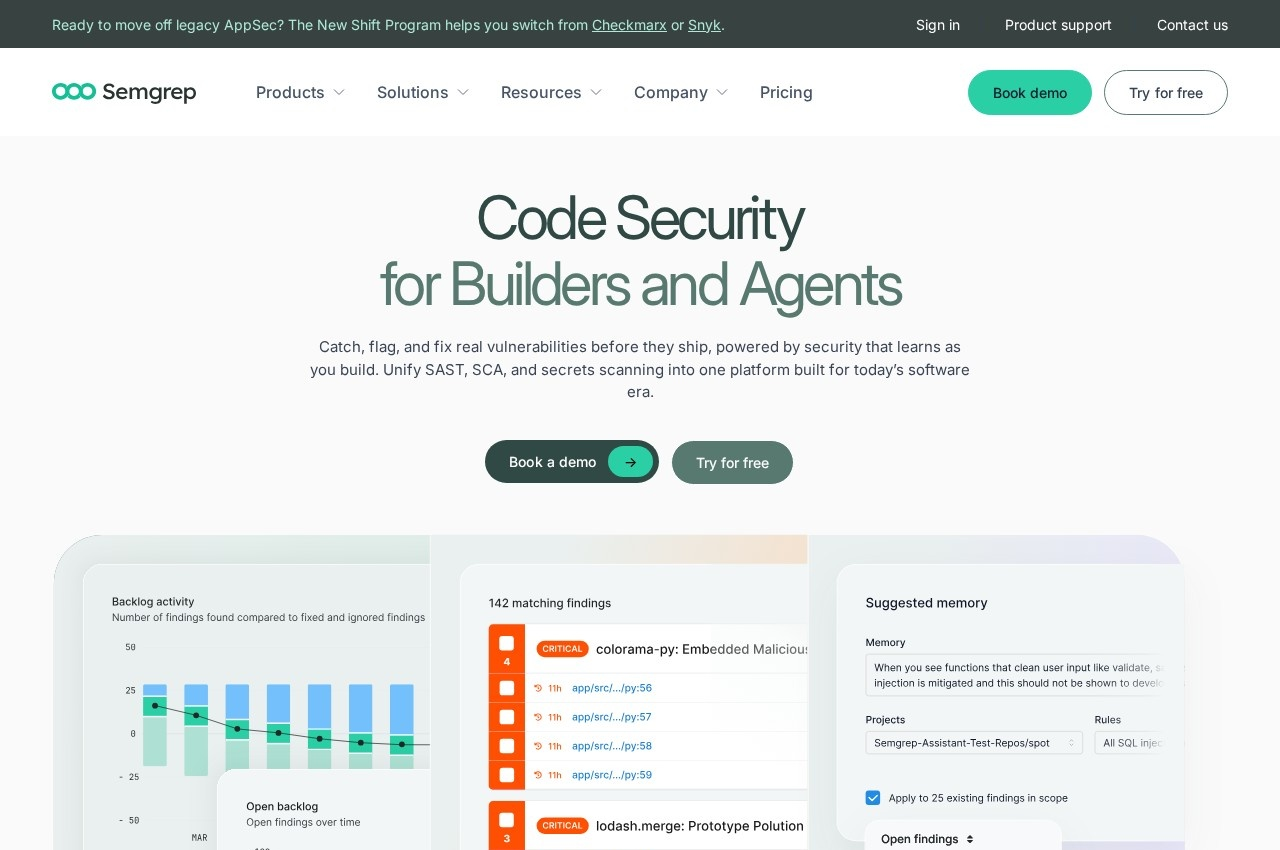
Semgrep scans source code for security and correctness problems using rules written in the syntax of the language being analysed, rather than in a separate query language. That design decision is what distinguishes it and it has a practical consequence worth understanding.
Static analysis tools have historically been extended only by specialists, because writing a custom rule meant learning an abstract syntax tree API and thinking in terms of parse trees. A rule in Semgrep looks like the code it matches, with wildcards, which means the developer who found the bug can write the rule preventing it from recurring.
That changes who owns the tool. A security team distributing findings from a scanner nobody else can modify is a bottleneck, whereas a team whose engineers add rules for their own codebase's known pitfalls builds a growing, organisation specific safety net that reflects real incidents rather than a vendor's generic checklist.
The product spans code scanning, supply chain analysis and secrets detection, each priced separately at thirty dollars per contributor per month, with a free tier covering up to ten repositories and ten contributors. Charging by contributor rather than by repository fits how the work is actually distributed.
Being open at the core matters here too, since a team can evaluate the engine and the rule format properly before committing to the hosted platform.
Key Features of Semgrep
- Static code analysis
- Rules written in code syntax
- Custom rule authoring by developers
- Supply chain dependency scanning
- Secrets detection
- Pull request integration
- Community rule registry
- Per contributor pricing
- Free tier for small projects
- Open source core engine
Semgrep Pricing
Free
Free
Up to 10 repositories and 10 contributors, with authentication via GitHub or GitLab.
Per product
$30
Code, Supply Chain and Secrets are each priced separately at this rate.
Semgrep Specifications
- Deployment
- Cloud Based
- On Premise
- Desktop
- Web App
- Linux
- Mac
- Built for
- Freelancers
- Small Business
- Medium Business
- Large Enterprise
- Support
- Knowledge Base
- Community
- Public API
- Yes
- Free trial
- Yes
- Free plan
- No
- Runs in browser
- No
- Customisable
- No
- Website
- semgrep.dev
Semgrep Videos
Semgrep Screenshots
Semgrep Comparisons
Semgrep Reviews
No reviews yet
Used Semgrep? Share your experience and help other buyers decide.
Semgrep FAQs
Alternatives to Semgrep
Other Secure Code Review Software recorded on the same fields.